

LDAP, or Lightweight Directory Access Protocol, is one of the quiet workhorses of modern IT. It rarely appears in headlines, yet it helps decide who can sign in, which groups a user belongs to, and which applications they can reach. If you have ever logged in once and gained access to email, file shares, and a company intranet, a directory service — very often reached through LDAP — was probably involved.
This guide explains LDAP in plain language, shows how authentication flows, compares LDAP with Active Directory, and covers security risks many guides skip, including LDAPS. By the end, you will know when LDAP fits, when it does not, and how to protect it.
What Is LDAP?
LDAP is an open protocol for accessing and maintaining directory information over a network. It is not itself a database product, and it is not a single vendor’s system. Instead, it defines how clients ask questions, how servers answer, and how directory entries are organized.
A directory is a specialized store optimized for reading, searching, and looking up information that changes relatively rarely. Typical entries describe people, groups, devices, printers, and applications. Each entry has attributes, such as a common name, email address, department, and group membership. Because directories are read far more often than they are written, LDAP is designed for fast searches, even in very large organizations.
LDAP grew out of the older X.500 directory standards, but it was deliberately lighter and easier to run over TCP/IP. Today it is supported by many operating systems, identity products, VPN gateways, and email systems. Standard LDAP traffic uses port 389, while secure LDAP, known as LDAPS, uses port 636.
How an LDAP Directory Is Organized
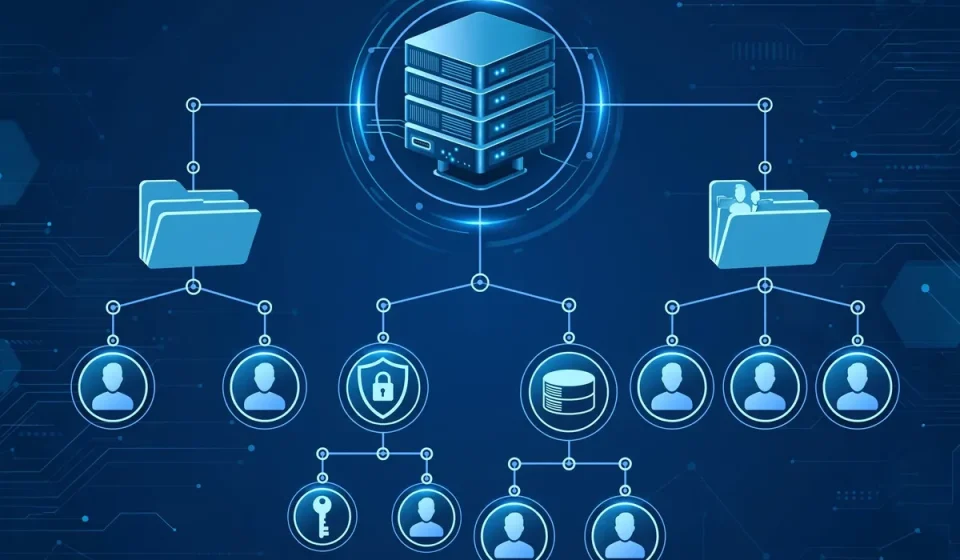
LDAP data is arranged in a tree, called the Directory Information Tree. At the top is a root, below it are domains or organizations, and below those are organizational units, groups, and individual entries. This hierarchy naturally mirrors a company structure, with branches for departments, regions, or teams.
Every entry has a distinguished name, or DN, that gives its full path in the tree. For example, a user entry might be uid=jchen,ou=People,dc=example,dc=com. The DN is unique, so no two entries share the same path. A relative distinguished name identifies an entry within its parent, while the full DN identifies it globally.
Entries use object classes that define which attributes they may or must have. A person entry, for instance, may require a surname and common name, while allowing a job title as an optional attribute. A schema defines these classes and attributes, keeping the directory consistent for every application that reads it.
How LDAP Authentication Works, Step by Step
A typical login works like this:
- The user enters a username and password in an application, such as a VPN portal or web app.
- The application connects to the LDAP server and searches for the username, to find the matching entry and its distinguished name.
- The application then attempts a bind — LDAP’s term for authenticating — using that distinguished name and the supplied password.
- The directory server checks the password against its stored credential. If it matches, the bind succeeds and the identity is confirmed.
- The application may then search again for group membership or roles, and use those results to decide what the user may do.
- Finally, the application grants or denies access based on its own authorization rules, not on LDAP alone.
This distinction matters. LDAP proves identity, but the application still decides authorization. A successful bind does not automatically mean a user should have administrator rights or access to sensitive files.
LDAP vs Active Directory: A Clear Comparison
People often confuse LDAP and Active Directory, but they are not the same thing. LDAP is a protocol. Active Directory is a Microsoft directory service that uses LDAP, among other protocols, for Windows networks. The table below summarizes the difference.
| Feature | LDAP | Active Directory |
|---|---|---|
| What it is | An open protocol | A Microsoft directory service |
| Vendor | Vendor-neutral | Microsoft |
| Main protocols | LDAP and LDAPS | LDAP, Kerberos, DNS, and Group Policy |
| Typical use | Cross-platform directory access | Windows domain identity and management |
| Authentication | Bind operations | Kerberos tickets, plus LDAP binds |
| Best for | Interoperability and integration | Central Windows administration |
In practice, many organizations use both. Active Directory can act as the main identity store, while other systems query it through LDAP. Learning how a Global Catalog in Active Directory works helps explain why searches across a large forest can be fast, because it holds a partial, searchable copy of objects from every domain.
Common LDAP Operations
Beyond authentication, LDAP supports a small set of core operations. A search finds entries matching a filter, such as all users in a department. An add creates a new entry, a delete removes one, and a modify changes attributes, for example when a user changes teams. A modify DN moves or renames an entry, while compare checks whether an entry has a particular attribute value without returning it.
These operations are powerful, so they must be tightly controlled. Ordinary users should normally read only the attributes they need, and only administrators should add, delete, or modify entries. Broad write access for an application account is a common mistake that can turn a small compromise into a directory-wide incident.
Real-World Use Cases for LDAP
Corporate single sign-on is a classic example: once a user is authenticated against the directory, multiple applications can trust that identity instead of keeping separate passwords. This is closely related to how SAML works for single sign-on, which builds a smoother login experience on top of a trusted identity source.
Email systems also rely on directories for address books and access control. VPNs, Wi-Fi networks, and firewalls can check group membership before allowing a connection. Developers use LDAP to centralize user management in custom applications, while universities and hospitals use it to manage staff, students, and devices in one place. In hybrid environments, LDAP often connects legacy systems to modern identity providers, acting as a bridge rather than being replaced overnight.
LDAP Security Risks and Why LDAPS Matters
This is the angle many short guides miss: LDAP, in its basic form, is not secure by default. Plain LDAP on port 389 can send credentials and directory data without encryption, so anyone able to observe the network path could capture sensitive information. Anonymous binds, if allowed, can also let unauthenticated users enumerate users and groups, giving an attacker a useful map of the environment.
Other risks include weak service accounts with excessive privileges, entries that expose more attributes than necessary, and applications that store LDAP credentials in plain text files. An attacker who obtains a service account may query the directory at scale, test passwords, or, if write access is granted, change group membership and gain higher privileges.
LDAPS solves the most urgent problem by wrapping LDAP in TLS encryption, usually on port 636. It protects credentials and data in transit and helps clients verify they are talking to the genuine directory server. StartTLS is another option: it begins as a plain connection, then upgrades to TLS before credentials are sent. Plain, unauthenticated LDAP binds for sensitive logins should be disabled wherever possible.
Encryption alone is not enough. Enforce least privilege for every LDAP account, require strong passwords or certificates for service accounts, and add multi-factor authentication in front of applications that rely on LDAP where possible. Multi-factor authentication (MFA) is especially valuable, because even a stolen directory password is far less useful if a second factor is required.
LDAP Security Best Practices
- Use LDAPS or StartTLS for all authentication and sensitive queries.
- Disable anonymous binds and limit what unauthenticated users can see.
- Give service accounts read-only access unless writes are truly required.
- Audit directory searches, binds, and changes, and alert on unusual patterns.
- Keep directory servers patched, and review group membership regularly.
- Store LDAP credentials in a secure vault, never in plain text files.
When LDAP Is Not the Best Choice
LDAP is excellent for centralized identity lookups, but it is not a general-purpose database. It suits rapidly changing transactional data poorly, and modern cloud applications may prefer OAuth, OpenID Connect, or SAML for federation, while still using a directory behind the scenes.
Conclusion
LDAP remains essential because identity remains essential. It gives organizations a standard, interoperable way to store, search, and authenticate users and groups across many systems. Used carefully — with LDAPS, least privilege, auditing, and multi-factor authentication — it can be both flexible and secure. Used carelessly, it can become an easy path for an attacker to map and exploit an organization.
Frequently Asked Questions
What does LDAP stand for?
LDAP stands for Lightweight Directory Access Protocol. It is a protocol for accessing and managing directory information, such as users, groups, and devices, over a network.
Is LDAP the same as Active Directory?
No. LDAP is an open protocol, while Active Directory is a Microsoft directory service that uses LDAP, Kerberos, DNS, and other protocols.
What is the difference between LDAP and LDAPS?
LDAP normally runs without encryption on port 389, while LDAPS runs LDAP over TLS, usually on port 636. LDAPS encrypts credentials and directory data in transit.
What is an LDAP bind?
A bind is the LDAP operation used to authenticate. A client supplies a distinguished name and password, and the server verifies them before allowing access to protected entries.
Is LDAP still used today?
Yes. LDAP is still widely used for corporate directories, VPN and Wi-Fi authentication, email systems, and application integration, often alongside SAML, OAuth, and OpenID Connect.

[…] them is a common source of configuration errors. For the directory behind them, see our guide to LDAP and how it stores and queries those […]