
When you search for a colleague in another part of a large company, or log on at a branch office far from headquarters, Active Directory still needs to find you quickly. That forest-wide lookup is the job of the global catalog. It is a special, searchable index of objects from every domain in an Active Directory forest, and it quietly supports logons, searches and applications every day.
This guide explains what the global catalog is, how it works, how it differs from an ordinary domain controller, which ports it uses, and how to secure it.
What Is the Global Catalog?
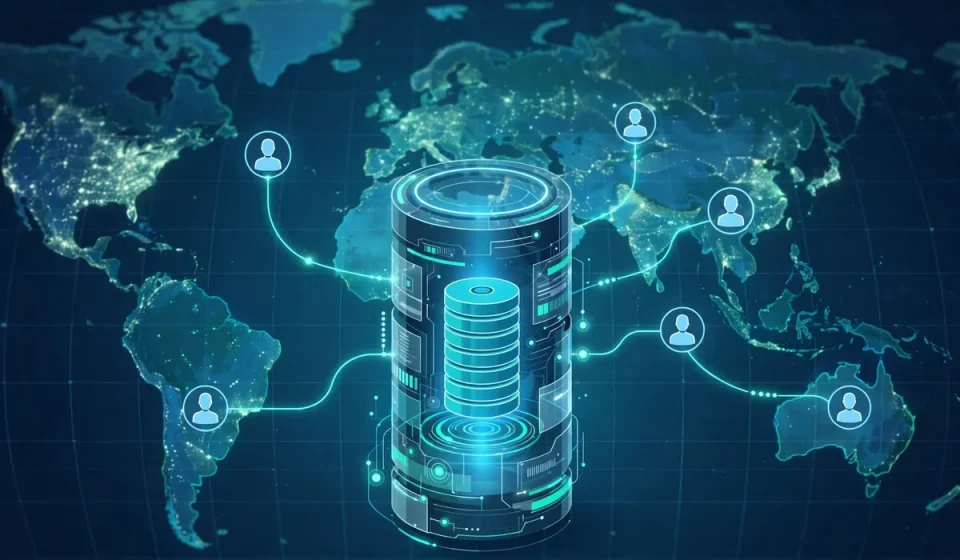
The global catalog is a distributed data repository hosted on selected domain controllers, called global catalog servers. Each global catalog server holds a full, writable copy of its own domain, plus a partial, read-only copy of objects from every other domain in the forest. That partial copy is called the partial attribute set. It contains the attributes administrators and applications search most often, such as user names, email addresses, group membership and department, rather than every attribute stored for each object.
Because of that design, a global catalog server can answer forest-wide questions without contacting a domain controller in every domain. If you search for a user, printer or group anywhere in the forest, the global catalog can usually return a result from its own index. In identity and access management, that single, searchable view of identities is what makes consistent access decisions possible across domains.
How the Global Catalog Works
When a global catalog server is promoted, it requests the partial attribute set for objects in other domains and replicates it through normal Active Directory replication. Changes to those attributes are then replicated to global catalog servers across the forest, so the index stays reasonably current without copying entire domain databases everywhere.
A client that needs a forest-wide search queries a global catalog server instead of an ordinary domain controller. The server searches its partial replica and returns matching objects, including the domain where each full object lives. Applications such as Exchange have historically relied on this behaviour to resolve recipients and distribution lists across domains, and directory-aware tools still use it for fast, forest-wide lookups.
There is an important limit to understand: the global catalog does not hold every attribute. If an application needs an attribute that is not in the partial attribute set, it must follow the referral to the object’s home domain and query a domain controller there. Planning which attributes are included, therefore, matters as much as planning how many servers you run.
Global Catalog vs. Domain Controller
Every global catalog server is a domain controller, but not every domain controller is a global catalog server. The difference is scope: an ordinary domain controller knows its own domain in full, while a global catalog server also knows the searchable attributes of the whole forest.
| Feature | Domain controller | Global catalog server |
|---|---|---|
| Scope | One domain | Entire forest |
| Own domain data | Full and writable | Full and writable |
| Other domains | Not held | Partial, read-only attribute set |
| Best for | Local authentication and domain changes | Forest-wide search and cross-domain logon checks |
Global Catalog Ports: 3268 and 3269
Global catalog queries do not use the standard LDAP ports alone. Port 3268 is used for unencrypted global catalog LDAP queries, and port 3269 is used for global catalog queries over SSL, often called LDAPS. Standard LDAP uses port 389, and LDAPS uses port 636, but those ports return results only from the domain controller’s own domain. If a firewall blocks 3268 and 3269, forest-wide searches will fail even when ordinary domain logons still work.
From a security perspective, treat 3268 as a port to restrict carefully. It can reveal directory information to anyone who can query it, so allow it only from trusted application servers, management hosts and other domain controllers. Prefer 3269, or an encrypted channel, whenever queries cross an untrusted network, and monitor unusual volumes of global catalog queries as a possible sign of directory enumeration.
Why Logons and Universal Groups Depend on It
When a user logs on in a multi-domain forest, Windows needs to know the user’s universal group membership to build a complete access token. That information is not stored in the user’s home domain alone, so the logon process contacts a global catalog server. If no global catalog server is reachable, logon may fail or fall back to cached credentials, depending on the configuration.
There is a useful exception: universal group membership caching. When this is enabled for a site, a domain controller can cache universal group memberships for users who have logged on at that site before. That helps branch offices survive a WAN outage, but it does not replace a global catalog server for first-time logons, forest-wide searches or new group assignments. Plan for both, not one instead of the other.
Securing the Global Catalog
A global catalog server is a high-value target because it concentrates searchable identity data. Protect it like any other domain controller, then add controls for its forest-wide role. Keep global catalog servers patched, restrict physical and remote administrative access, and never place one in an untrusted network segment simply to improve search speed. A compromised global catalog server can expose user, group and service information across domains, which attackers use to plan lateral movement.
Also review who can query the directory. Anonymous LDAP access should be disabled, service accounts should have only the permissions they need, and privileged group membership should be audited regularly. Adding multi-factor authentication for administrator logons reduces the chance that a stolen password becomes a forest-wide compromise. Finally, log global catalog queries and authentication failures centrally, so unusual enumeration or repeated failed searches are visible rather than silent.
How to Check and Enable a Global Catalog Server
To check a server, open Active Directory Sites and Services, expand the site and the server, open the NTDS Settings object, and look for the Global Catalog setting. You can also confirm that the server registers the global catalog service records in DNS, and that clients in the site can resolve and reach it on ports 3268 and 3269. If a server was recently promoted, allow time for the partial attribute set to replicate before judging its search results.
Placement Checklist: How Many Global Catalog Servers Per Site?
This is the question most short guides leave unanswered. The safe starting rule is simple: every Active Directory site that has users, applications or domain controllers should have at least one global catalog server, and larger or more critical sites should have two. A single site-wide outage, patching window or hardware failure should not remove forest-wide search and logon support for everyone at that location.
Use this checklist before you promote or demote a global catalog server: first, confirm the site has users who log on locally or applications that perform forest-wide searches; second, check whether the WAN link to another site is slow, unreliable or congested at logon time; third, require two global catalog servers where headcount, application load or business criticality is high; fourth, enable universal group membership caching as resilience, not as a substitute for a local server; and fifth, verify ports 3268 and 3269 and replication health after any change.
Worked Example: A Three-Site Company
Consider a company with headquarters (500 users), a regional office (120 users) and a small branch (25 users). Headquarters gets two global catalog servers for redundancy and application load. The regional office gets two as well if its WAN link is unreliable, or one plus universal group membership caching if the link is fast and stable. The small branch gets one global catalog server if it has a local domain controller and regular logons. The total is therefore five or six global catalog servers: redundancy follows users, applications and link risk.
Troubleshooting Common Global Catalog Problems
If forest-wide searches fail, first check that at least one global catalog server is reachable from the client and that ports 3268 and 3269 are open. Next, verify replication: a server that has not replicated the partial attribute set cannot answer accurately. Finally, confirm the attribute you need is actually in the partial attribute set; if it is not, the search must be directed to the object’s home domain instead.
Frequently Asked Questions
What is the global catalog in Active Directory?
It is a searchable index, hosted on global catalog servers, containing a full copy of their own domain and a partial, read-only copy of objects from every other domain in the forest.
Is a global catalog server the same as a domain controller?
No. Every global catalog server is a domain controller, but an ordinary domain controller only holds full data for its own domain, not the forest-wide partial attribute set.
What ports does the global catalog use?
It uses port 3268 for LDAP queries and port 3269 for LDAP over SSL. Standard LDAP ports 389 and 636 are domain-specific, not forest-wide.
Do I need a global catalog server in every site?
As a practical rule, yes for sites with users or forest-wide applications, with two servers in larger or more critical sites. Universal group membership caching improves resilience, but it does not fully replace a local global catalog server.
Why would a global catalog search miss an attribute?
The attribute may not be included in the partial attribute set. In that case, query the object’s home domain directly, or ask an administrator to add the attribute to the partial attribute set after testing the replication impact.