
IPsec is the set of rules that keeps internet traffic private and tamper-proof. Short for Internet Protocol Security, it is the technology behind many of the virtual private networks (VPNs) that businesses use to connect offices, protect remote workers and link systems to the cloud. If you have ever wondered how a company lets staff work from home without exposing its internal systems to the internet, IPsec is very often the answer.
What Is IPsec?
IPsec is a suite of protocols that works at the network layer of the internet, the layer that moves data packets between devices. Unlike tools that protect a single application, IPsec protects everything travelling between two points: every packet is encrypted so outsiders cannot read it, and authenticated so the receiver can be sure it has not been altered and really came from the claimed sender.
Because it sits at the network layer, IPsec is transparent to applications. Email, file sharing, databases and web tools all run over it without any change. That is why it became the standard choice for site-to-site VPNs connecting offices, and why it is built into most business routers, firewalls and operating systems.
How IPsec Works: The Two Main Protocols
IPsec relies on two core protocols that do different jobs. The Authentication Header (AH) proves where a packet came from and that it has not been changed, but it does not encrypt the contents. The Encapsulating Security Payload (ESP) both encrypts the data and authenticates it, so the contents stay secret as well as trustworthy. In practice, almost all modern IPsec deployments use ESP, because confidentiality matters as much as authenticity.
Before any data flows, the two ends must agree on how to protect it. That negotiation is handled by the Internet Key Exchange (IKE), which sets up a secure channel, exchanges keys and agrees on the encryption algorithms. Once the security association is established, traffic flows through an encrypted tunnel until the keys expire and are refreshed.
Transport Mode vs Tunnel Mode
| Mode | What it protects | Typical use |
|---|---|---|
| Transport mode | Only the data payload of each packet; the original header stays visible | Host-to-host communication between two computers |
| Tunnel mode | The entire original packet, wrapped inside a new packet | Site-to-site VPNs between offices, and remote-access VPNs |
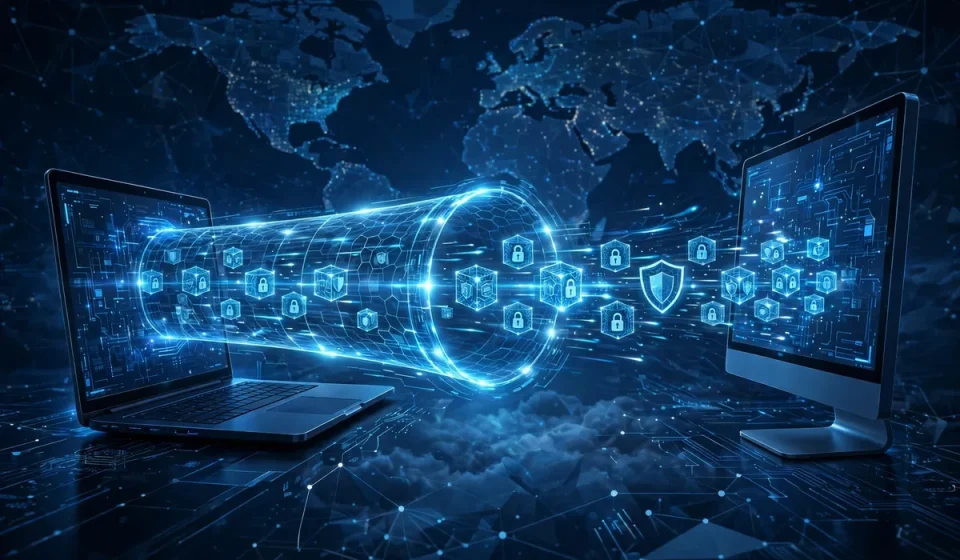
Tunnel mode is what most people mean when they talk about an IPsec VPN. An office router wraps all traffic bound for another office inside an encrypted tunnel, so anyone watching the internet sees only scrambled data flowing between the two gateways. Inside the tunnel, the original addresses and data remain intact, so the two offices behave as if they were on one private network.
How an IPsec VPN Works, Step by Step
First, a user or office gateway initiates a connection to the VPN gateway. Second, IKE negotiates the security settings and exchanges keys, with both sides proving their identity, usually with certificates or a pre-shared key. Third, a secure tunnel is established and traffic starts flowing through it, encrypted with ESP. Fourth, keys are regularly renegotiated so that even if one key were somehow exposed, only a small amount of traffic would be at risk. Finally, when the session ends or goes idle, the tunnel is torn down.
From the user’s point of view, none of this is visible. A remote worker opens their laptop, the VPN connects, and internal applications simply work, with every packet protected in transit.
IPsec vs SSL VPN: Which Should You Use?
IPsec VPNs and SSL (or TLS) VPNs solve similar problems in different ways. IPsec works at the network layer and protects all traffic between two points, which makes it ideal for always-on connections between offices and for giving remote workers full network access. SSL VPNs work at the application layer, usually through a web browser or a lightweight client, and are simpler to set up for giving a contractor or employee access to a single web application.
Many organisations use both: IPsec for permanent office-to-office links and for staff who need broad access, and SSL VPN for quick, browser-based access to specific tools. The right choice depends on who needs access, to what, and how much control you need over their device.
Real-World Examples
A retail chain with fifty stores uses IPsec tunnels from each store back to head office, so tills, stock systems and staff devices all communicate over encrypted links instead of the open internet. A hospital lets radiologists read scans from home through an IPsec VPN, so patient images travel encrypted and only authenticated devices can reach the imaging system. A company migrating to the cloud uses IPsec to connect its office network to its cloud environment, extending its private network securely rather than exposing cloud resources publicly.
IPsec also pairs naturally with other controls. A network firewall at each site controls which traffic may enter the tunnel in the first place, network security software monitors the tunnelled traffic for threats, and a zero-trust network access approach can add per-application checks on top of the VPN for sensitive systems.
Advantages and Limitations
IPsec’s strengths are maturity, broad support and network-wide protection. It is an open standard supported by virtually every enterprise router and firewall, it protects all traffic rather than one application, and it has been battle-tested for decades. Its limitations are worth knowing too: it can be fiddly to configure, especially through firewalls that block its traffic; it does not protect data once it arrives at its destination; and on its own it does not check whether the device connecting is healthy or compliant. That is why IPsec is usually combined with strong authentication, device checks and monitoring rather than trusted on its own.
Setting Up IPsec: What to Get Right
Use certificates rather than shared passwords where possible, because certificates are harder to steal and easier to revoke. Choose modern encryption, such as AES with strong key lengths, and avoid outdated algorithms that are now considered weak. Keep firmware and software updated on VPN gateways, since they are internet-facing and a popular target. Log VPN connections and review them, watching for logins at odd hours, from unusual locations or from unexpected devices. Finally, apply the principle of least privilege: a VPN user should reach only the systems their job requires, not the entire network.
Common Mistakes to Avoid
The most common IPsec mistakes are using weak pre-shared keys that are shared between many users and never changed, leaving outdated encryption enabled for compatibility, and granting VPN users unrestricted access to the whole internal network. Another frequent error is forgetting that the tunnel protects data only in transit: once traffic exits the tunnel, it still needs the usual protections, such as encryption at rest and access controls, on the systems it reaches.
Frequently Asked Questions
What is IPsec in simple terms?
IPsec is a set of internet protocols that encrypts and authenticates network traffic, so data travelling between offices, remote workers and cloud systems stays private and tamper-proof.
Is IPsec the same as a VPN?
Not quite. IPsec is the technology that many VPNs use. A VPN is the secure connection itself; IPsec is one of the main protocols used to build it.
What is the difference between IPsec transport mode and tunnel mode?
Transport mode protects only the data inside each packet, while tunnel mode encrypts the entire original packet inside a new one. Tunnel mode is the standard choice for site-to-site and remote-access VPNs.
Is IPsec still secure?
Yes, when configured with modern encryption such as AES and strong authentication. Older algorithms and weak shared keys are the real risk, so keep configurations current.
Do I need IPsec if I already use HTTPS?
HTTPS protects traffic to one website at a time. IPsec protects all traffic between two networks or devices, which is what you need for office connections, remote access and cloud links.