
When a company talks about staying safe online, it usually mentions firewalls, passwords and antivirus software. Those tools matter, but they do not watch themselves. Somebody has to monitor them, notice when something looks wrong, and act before a small problem becomes a serious incident. That ongoing work is called SecOps, short for security operations.
SecOps is the people, processes and tools that monitor systems and respond to threats day to day. It is not a single product you can buy, and it is not a one-off project. It is the daily routine of keeping an organisation’s computers, networks, cloud accounts and data safe while normal work continues. This article explains what a SecOps team actually does, how it differs from related jobs, and how a small company can cover it without a large team.
What SecOps Means in Plain Words
Think of SecOps as the security watch team for an organisation. Just as a building needs people who watch the entrances, check alarms and respond to emergencies, a digital organisation needs people who watch its systems. They look for signs of attack, misuse, failure or unusual behaviour, and they decide what needs attention now and what can wait.
SecOps combines three things. People make judgements, investigate alerts and respond to incidents. Processes give them a consistent way to handle those events, so the same kind of problem is not handled differently every time. Tools collect logs and alerts, and help the team see what is happening across many systems at once. Without all three, security operations falls apart: tools without people generate noise, people without processes improvise under pressure, and processes without tools leave the team blind.
What a SecOps Team Actually Does All Day
Monitoring comes first. The team watches alerts from systems, networks, endpoints and cloud services, looking for events that could indicate an attack or a fault. This is continuous work, because threats do not keep office hours, and a delay in noticing an intrusion can make the difference between a contained incident and a major breach.
Next is triage, which means sorting alerts into real problems, false alarms and low-priority noise. Not every alert is an attack. Many are routine events, misconfigurations or harmless activity. Triage is the skill of deciding quickly and fairly what deserves a deeper investigation, and it is one of the most important SecOps jobs.
When triage finds something real, the team moves to incident response. That means containing the problem, for example by isolating an affected computer or disabling a compromised account, understanding how far it spread, removing the cause, and restoring normal service. Good incident response is calm, documented and practised, not improvised during a crisis.
Between incidents, SecOps teams do threat hunting, which is proactively searching for signs of attack that alerts may have missed. They also support vulnerability management by helping to prioritise which weaknesses should be fixed first, based on how exposed they are and how likely they are to be exploited. Finally, they keep detections and logging healthy: making sure logs are collected, alerts are tuned, and the tools themselves are working. If logging stops, the team is effectively blind, even if everything else looks fine.
The SOC: The Home of SecOps
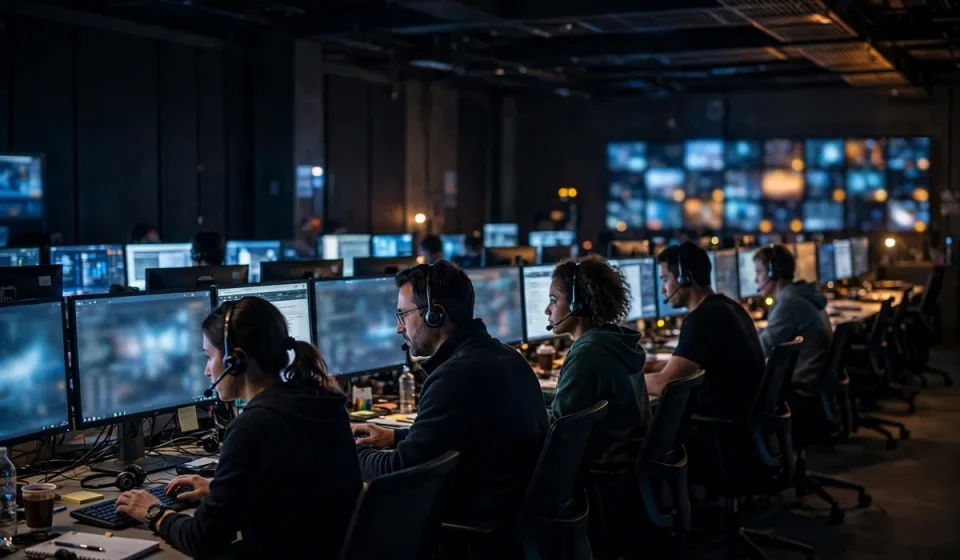
Much of this work happens in a security operations centre, usually called a SOC. A SOC is not necessarily a dramatic room full of screens, although larger organisations may have one. It is the function, and often the team, responsible for monitoring and response. In a large company, the SOC may run around the clock in shifts. In a smaller company, it may be a few people who share monitoring duties alongside other work, or an external provider that performs the same function remotely.
The SOC model matters because security monitoring needs focus and continuity. Alerts need an owner, incidents need a clear chain of command, and lessons from one incident need to feed back into better detections. Whether the SOC is in-house, outsourced or a mix of both, its job is the same: watch, understand, respond and improve.
SecOps vs DevSecOps: An Honest Distinction
SecOps and DevSecOps sound similar, but they describe different emphases. SecOps is about operations and run-time security: monitoring live systems, responding to incidents and keeping defences working after software is deployed. DevSecOps is about building security into development: helping developers write safer code, test for vulnerabilities early, and automate security checks in the software pipeline.
The two overlap and should cooperate, but they are not interchangeable. A strong DevSecOps programme can reduce the number of vulnerabilities that reach production, but it cannot watch for attacks against a live system at 2 a.m. Likewise, a strong SecOps team can respond well to incidents, but it cannot fix insecure code at its source. Organisations need both perspectives: security built in during development, and security watched over during operation.
SecOps vs IT Operations
IT operations, often called IT ops, is focused on keeping systems running: making sure services are available, performance is acceptable, and users can work. SecOps is focused on keeping systems safe: making sure they are not compromised, misused or leaking data. These goals usually align, but they can pull in different directions. A quick fix that restores a service might also reopen a security risk, while a strict security control might slow down a legitimate task.
That tension is why the two teams must cooperate rather than work in isolation. IT ops knows how systems are built and used, which helps SecOps understand what is normal and what is suspicious. SecOps knows where the risks are, which helps IT ops avoid changes that create new exposure. When they share information, agree on priorities and practise incident response together, both availability and security improve.
The Key Tools, in General Terms
SecOps teams rely on a few categories of tools, and it is more useful to understand the categories than to memorise product names. A SIEM, or security information and event management system, collects logs and alerts from many sources into one place, so the team can search and correlate events. EDR, or endpoint detection and response, monitors individual computers and servers for suspicious behaviour and helps analysts investigate and isolate them.
Ticketing and case management tools track incidents from first alert to final closure, so nothing is lost and lessons are recorded. Around these core tools sit vulnerability scanners, threat intelligence feeds and automation tools that handle repetitive tasks. The right mix depends on the size and complexity of the organisation, but the principle is the same: tools should help people see clearly and act quickly, not bury them in data.
The Alert-Fatigue Problem
The classic SecOps pain is alert fatigue. When tools generate too many low-quality alerts, analysts become overwhelmed, start to ignore warnings, or spend all their time closing false positives instead of investigating real threats. This is not just an annoyance; it is a genuine security risk, because a real attack can hide in a flood of noise.
Dealing with alert fatigue is a core SecOps skill. It means tuning detections so they fire only when they matter, combining related alerts into a single case, removing alerts for known harmless activity, and regularly reviewing which alerts actually led to useful action. Good SecOps is not measured by the number of alerts produced, but by how quickly real incidents are found and how few are missed.
SecOps in the Cloud
Cloud computing changes SecOps, but it does not remove the need for it. In the cloud, the provider secures the underlying infrastructure, while the customer remains responsible for its own accounts, data, configurations and access. That shared responsibility means SecOps must monitor cloud accounts, cloud storage, identities and software-as-a-service applications, not just office networks and servers.
Cloud SecOps also has to deal with speed and scale. Resources can be created and deleted in minutes, and a misconfigured cloud service can expose data to the internet almost instantly. Effective cloud monitoring therefore focuses on identity activity, configuration changes, unusual data movement and access from unexpected places, alongside traditional network and endpoint signals. The tools may be different, but the discipline is the same: watch continuously, triage carefully and respond quickly.
How a Small Company Covers SecOps Without a Team
Many small companies cannot staff a full SOC, and that does not mean they must ignore security operations. One common route is a managed detection and response service, often called MDR, or another managed security service. In this model, an external provider monitors the company’s systems, investigates alerts and helps respond to incidents, usually for a regular fee. The company still owns its risks and decisions, but it gains specialist coverage it could not hire alone.
Whether in-house or outsourced, a small company should still cover the basics: central logging from its most important systems, alerting for the highest-risk events, a simple incident response plan that names who does what, and a regular review of accounts, access and backups. SecOps does not have to start big. It has to start clear, consistent and focused on the risks that matter most, and grow as the organisation grows.
SecOps is, in the end, the unglamorous work that makes all other security measures useful. Firewalls, encryption and training only help if somebody is watching, judging and responding when they are tested. That is what security operations does all day, and why it deserves attention even when nothing dramatic is happening. Quiet days in SecOps are not wasted days; they are the result of monitoring, tuning and preparation working as intended.
Frequently Asked Questions
What is SecOps?
SecOps, short for security operations, is the people, processes and tools that monitor systems and respond to threats day to day. It covers alert monitoring, triage, incident response, threat hunting and keeping security detections and logging working.
What is a SOC?
A SOC, or security operations centre, is the team or function responsible for security monitoring and response. It may be an in-house team working in shifts, a small group sharing the duty, or an external provider performing the same monitoring and response work remotely.
What is the difference between SecOps and DevSecOps?
SecOps focuses on operations and run-time security, such as monitoring live systems and responding to incidents. DevSecOps focuses on building security into software development, such as testing code early and automating security checks in the development pipeline.
What causes alert fatigue in SecOps?
Alert fatigue happens when security tools generate too many low-quality or false-positive alerts, overwhelming analysts so that real threats are harder to spot. It is reduced by tuning detections, combining related alerts, removing noise and regularly reviewing which alerts lead to useful action.
How can a small company cover SecOps without a security team?
A small company can use a managed detection and response service, or another managed security service, to monitor systems and help respond to incidents. It should also keep central logging, alerting for high-risk events, a simple incident response plan and regular reviews of accounts, access and backups.