
An on-path attack is a quietly dangerous threat. You can type a familiar address, see a normal-looking website, and still have someone sitting in the middle of your connection, watching, copying, or changing what passes between you and the site you meant to reach. This guide explains what an on-path attack is, how it works, what attackers can steal or change, its warning signs, and how to stop it.
What Is an On-Path Attack?
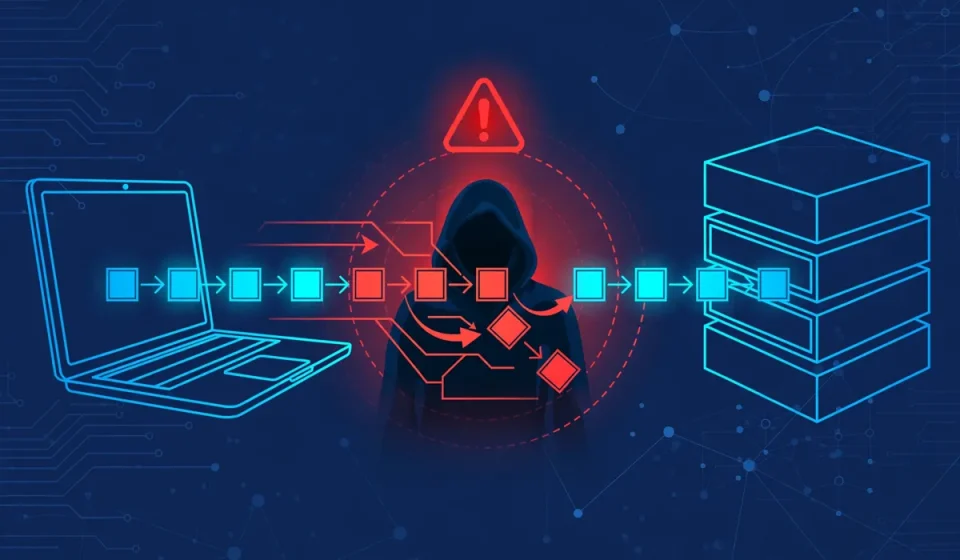
An on-path attack happens when an attacker positions themselves on the path between two parties who are communicating, usually between your device and a website, app, or server. Instead of breaking into your computer directly, the attacker intercepts traffic as it travels across a network. From that position, they can read messages, steal credentials, capture session data, or alter information before it reaches its destination.
On-path attack is the modern name for what used to be called a man-in-the-middle attack. The older name described the same idea, but the newer term describes the attacker’s position more accurately. The victim often notices nothing unusual: the website still loads, the login still works, and messages still arrive. The attacker is not trying to stop the conversation, but to stay hidden inside it.
How an On-Path Attack Works
Most on-path attacks follow a simple pattern. First, the attacker gains a position on the same network path as the victim, or gains control over part of the network routing. Second, they intercept traffic that would normally go straight to its destination. Third, they either watch that traffic passively or relay it while reading or changing it. Finally, they use what they collect, such as passwords, session cookies, payment details, or private messages.
Think of it like a letter passing through a dishonest sorting office. The letter still reaches its address, but someone has opened it, copied its contents, or changed a few words along the way.
Public Wi-Fi: The Most Common Starting Point
Public Wi-Fi is a common starting point because it is open, shared, and often unencrypted. In a coffee shop, airport, hotel, or train station, many devices connect to the same wireless network. If that network is not properly secured, an attacker on the same network may be able to see traffic that is not protected by encryption.
Attackers also create evil twin networks: fake Wi-Fi hotspots with a name that looks like a trusted network, such as a hotel or airport. When a device connects automatically, or a user chooses the fake network by mistake, traffic can pass through the attacker’s equipment. Treat public Wi-Fi as untrusted, avoid sensitive work on it when possible, and use HTTPS and a trusted VPN.
ARP Spoofing and DNS Spoofing in Plain Words
Two common techniques help attackers get into the middle of a connection: ARP spoofing and DNS spoofing.
ARP spoofing works on a local network. Devices use ARP, or Address Resolution Protocol, to find each other by matching a network address to a physical address. In ARP spoofing, the attacker sends false ARP messages that tell other devices, in effect, “send traffic meant for the router to me instead.” Traffic then flows through the attacker, who forwards it to the real router so the connection still appears to work.
DNS spoofing, also called DNS poisoning, attacks the lookup that turns a website name into an address. When you type a website name, your device asks a DNS service where to go. If an attacker can corrupt or fake that answer, your device may be sent to a malicious server that looks like the real site, where you might enter credentials into a convincing copy.
Session Hijacking Explained Simply
Session hijacking is another way an on-path attacker takes over an account without needing your password. When you log in to a website, the site usually gives your browser a session token, often stored as a cookie, that tells the site “this browser is already signed in.”
If an attacker captures that session token from unencrypted traffic or a compromised network, they can present it as if they were you. The website may then let them into your account, even though they never knew your password. That is why secure, encrypted connections matter, and why you should log out properly and not stay signed in on shared devices.
What Attackers Can Steal or Change
An attacker in the middle of a connection can steal login credentials, email contents, private messages, payment card details, account numbers, security codes, and files sent over an unprotected connection. They may also capture session tokens that let them impersonate you.
Stealing is not the only risk. An on-path attacker can also change data in transit: replace a download with a malicious file, alter a payment instruction, insert misleading text into a message, or redirect you to a fake login page. In business settings, changed invoices and altered bank details are especially dangerous, because the victim may act on false information without realizing it. Intercepted details can also be reused later for convincing phishing messages, which overlap with social engineering attacks.
Warning Signs of an On-Path Attack
On-path attacks are designed to be invisible, so no single sign proves one is happening. Still, watch for these clues:
- Browser warnings about an invalid, expired, or mismatched security certificate.
- A website that suddenly uses HTTP instead of HTTPS, or shows “Not Secure” in the address bar.
- Being logged out unexpectedly, or asked to log in again on a site where you were already signed in.
- Pages that look slightly wrong, load slowly on a normally fast network, or contain unfamiliar pop-ups.
- A Wi-Fi name that is almost, but not quite, the official network name.
- Account settings changed, messages you did not send, or transactions you do not recognize.
Any one of these can have an innocent explanation, but a certificate warning should never be clicked through casually. On a banking, email, or work site, stop and verify the site through another trusted route before entering credentials.
How to Stop an On-Path Attack: Practical Defenses
Use HTTPS Everywhere
HTTPS encrypts traffic between your browser and a website, so an attacker in the middle should see scrambled data rather than readable passwords and messages. Always look for HTTPS and the padlock symbol, especially on login, banking, shopping, and email sites, and do not enter sensitive information on a plain HTTP site.
Use a Trusted VPN on Untrusted Networks
A virtual private network, or VPN, creates an encrypted tunnel for your traffic. On public Wi-Fi, a reputable VPN can protect your data from other people on the same network, even if the local network is insecure. A VPN protects the connection, not the website itself, so you should still check for HTTPS.
Turn On Multi-Factor Authentication
Multi-factor authentication, or MFA, requires a second check in addition to your password, such as a code from an authenticator app or a hardware key. Even if an attacker steals your password, MFA can stop them from signing in, removing the easiest path into your accounts.
Use HSTS and Check Certificates
HTTP Strict Transport Security, or HSTS, tells browsers to connect to a website only over HTTPS. For website owners, enabling HSTS reduces the chance that a user can be downgraded to an unencrypted connection. For users, the lesson is simpler: pay attention to certificate warnings, do not accept unknown certificates, and keep your browser and operating system updated.
Avoid Open Wi-Fi for Sensitive Work
When possible, avoid banking, work email, admin panels, and payments on open Wi-Fi. If you must use a public network, use a VPN, stick to HTTPS sites, and log out when you finish. For remote work, zero-trust network access offers a stricter model than a traditional VPN by checking identity and device before granting access to individual applications.
Keep Devices and Networks Patched
Software updates often fix flaws attackers use to spoof networks, hijack sessions, or bypass encryption. Keep your browser, operating system, router firmware, and apps updated, and use home or office Wi-Fi with a strong password and modern encryption.
What to Do If You Suspect an On-Path Attack
Disconnect from the suspicious Wi-Fi network and do not log in again from it. From a trusted network and device, change passwords for important accounts, starting with email, since email is often used to reset other accounts. Turn on MFA where it is not already enabled, review recent activity, and log out of other sessions if the service allows it. If work systems are involved, tell your IT or security team promptly. If payment details may have been exposed, contact your bank or card provider.
Conclusion
An on-path attack succeeds by hiding in a connection you trust. By using HTTPS everywhere, a trusted VPN on public networks, multi-factor authentication, certificate checks, and sensible caution around open Wi-Fi, you make it far harder for an attacker to sit in the middle of your traffic.
Frequently Asked Questions
What is an on-path attack in simple terms?
An on-path attack is when an attacker secretly sits between you and a website or service, so your traffic passes through them. They can read, copy, or change that traffic while the connection still appears to work normally.
Is an on-path attack the same as a man-in-the-middle attack?
Yes. On-path attack is the modern name for a man-in-the-middle attack. Both terms describe an attacker positioned in the middle of a communication between two parties.
Can HTTPS stop an on-path attack?
HTTPS greatly reduces the risk, because it encrypts traffic between your browser and the website. An attacker may still see that a connection exists, but should not be able to read passwords or messages easily. HTTPS does not help if you ignore certificate warnings or enter credentials on a fake site.
Does a VPN protect me from an on-path attack?
A trusted VPN helps on untrusted networks by encrypting your traffic through a tunnel, which makes it much harder for someone on the same public Wi-Fi network to intercept it. A VPN is not a complete solution on its own, so you should still use HTTPS and multi-factor authentication.
How can I tell if I am the victim of an on-path attack?
Look for certificate warnings, unexpected logouts, sites switching from HTTPS to HTTP, unfamiliar Wi-Fi networks, and account activity you do not recognize. If you suspect an attack, disconnect, change important passwords from a trusted device, and check your accounts carefully.