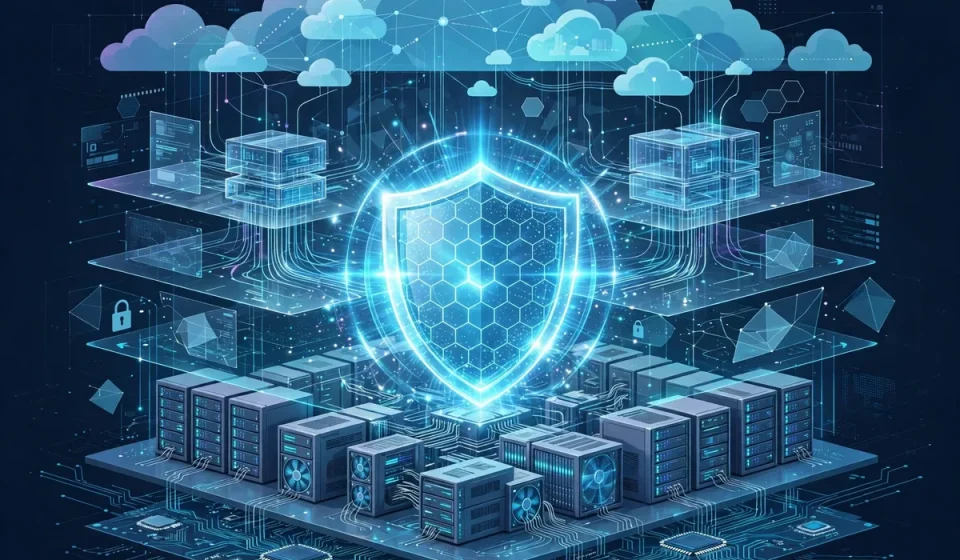

As organizations move workloads to virtualized and cloud environments, security must move with them. A security virtual appliance is a security solution delivered as software that runs on a virtual machine, rather than as a dedicated hardware box. It brings familiar protections, such as firewalls, intrusion prevention and web filtering, into environments where hardware appliances cannot easily go.
This guide explains what a security virtual appliance is, how it differs from hardware and cloud-native security, its benefits and limitations, and the use cases where it makes the most sense.
What Is a Security Virtual Appliance?
A security virtual appliance is a pre-packaged, hardened virtual machine image that performs a security function. Vendors provide it as a downloadable image for platforms such as VMware, Hyper-V, KVM or public cloud marketplaces. Once deployed, it runs like any other virtual machine, but its operating system and application are tuned for security, with unnecessary services removed and management interfaces secured.
Common examples include virtual firewalls, virtual intrusion prevention systems, virtual web application firewalls, secure web gateways and virtual VPN concentrators. In a data center or cloud, these appliances inspect traffic between virtual machines, between cloud segments, or between users and applications, applying the same policies that a hardware appliance would enforce at a physical network boundary.
Virtual Appliance vs. Hardware Appliance vs. Cloud-Native Security
Hardware appliances offer dedicated performance and physical isolation, but they require procurement, rack space, power and maintenance, and they cannot be deployed inside a cloud provider’s network where you do not control the hardware. Cloud-native security services, such as managed firewalls and security groups, are deeply integrated with the cloud platform and scale automatically, but they are specific to that provider and may not match an organization’s existing policies or tools.
Virtual appliances sit between these models. They are portable across virtual environments, they can be deployed quickly from a template, and they allow organizations to use the same vendor, policies and management console in their own data center and in the cloud. That consistency is valuable for teams that operate hybrid environments and want one way of working everywhere.
Benefits of Security Virtual Appliances
Speed and flexibility are major benefits. A virtual appliance can be deployed in minutes, cloned for testing, scaled by adding instances, and moved between hosts or regions as needs change. There is no hardware lead time and no need to visit a data center to install a device. Licensing is usually subscription-based, which aligns cost with usage and avoids large upfront hardware purchases.
Virtual appliances also support segmentation and micro-segmentation. By placing an appliance between virtual networks or application tiers, organizations can enforce east-west traffic controls, so that a compromise in one segment does not spread freely to others. Central management, snapshots for backup and rollback, and integration with virtualization platforms make operations more consistent than managing many scattered hardware devices.
Limitations to Consider
Virtual appliances share the underlying host’s resources, so performance depends on correct sizing, CPU, memory and network allocation, and on the host’s own security. A compromised hypervisor or an overcommitted host can affect every appliance on it. Throughput can also be lower than a dedicated hardware appliance designed for a specific line rate, so high-volume environments need careful testing.
Licensing, patching and lifecycle management still require discipline. A virtual appliance is software, and it must be updated, monitored and backed up like any critical system. Organizations should also verify that a virtual appliance is supported and certified for their chosen hypervisor and cloud platform, because not every image works everywhere.
Comparing Security Deployment Models
| Model | Deployment Speed | Portability | Best For |
|---|---|---|---|
| Hardware appliance | Slow, needs procurement and install | Low, tied to location | High-throughput physical perimeters |
| Security virtual appliance | Fast, from a template | High across virtual platforms | Hybrid and virtualized environments |
| Cloud-native service | Very fast, managed | Low, provider-specific | Single-cloud, cloud-first teams |
| Agent-based security | Fast per host | High, follows the workload | Endpoint and workload protection |
Most mature organizations use a combination. A hardware firewall may guard the physical perimeter, virtual appliances may protect virtual segments and cloud workloads, and cloud-native controls may handle provider-specific services. The goal is consistent policy across all of them, not a single tool for every problem.
Common Use Cases
Protecting virtualized data centers
In a virtualized data center, traffic between virtual machines may never leave the host, so a physical firewall cannot see it. A virtual firewall placed at the virtual switch or between segments can inspect that east-west traffic and enforce segmentation policies.
Securing cloud workloads
Virtual appliances deployed in public cloud virtual networks can provide firewalling, intrusion prevention and VPN termination with familiar policies, especially during migration when teams are learning cloud-native tools. They are also useful in multi-cloud designs where a single vendor’s appliance provides consistency across providers.
Branch and remote access
Virtual appliances can serve as VPN concentrators, secure web gateways or remote-access brokers for distributed teams, without requiring hardware at each location. Combined with centralized management, they simplify policy updates for many sites.
Test, development and disaster recovery
Because virtual appliances can be cloned and snapshotted, they are well suited to test environments that must mirror production security, and to disaster-recovery sites that need to be ready quickly without maintaining duplicate hardware.
Deploying a Security Virtual Appliance Well
Start with a clear design: which traffic the appliance will inspect, where it sits in the network, and how it fails if it becomes unavailable. Fail-closed designs block traffic on failure, which is safer but can cause outages, while fail-open designs allow traffic, which preserves availability but weakens security. Choose deliberately, and test failover.
Size the appliance for peak traffic, not average load, allocate dedicated resources where the vendor recommends, and monitor CPU, memory, throughput and dropped packets. Keep the appliance patched, back up its configuration, restrict management access to trusted networks and administrators, and log its activity to your central security monitoring system. Finally, review whether a cloud-native alternative would be simpler or cheaper for a given workload, and use virtual appliances where their portability and consistency genuinely add value.
For the infrastructure these appliances protect, see this overview of what data centers are and how they work. Perimeter concepts that apply to virtual and physical firewalls alike are explained in this guide to what a network firewall does, and for a modern secure-access architecture, read what SASE is and how it works.
Frequently Asked Questions
What is a security virtual appliance?
It is a security solution delivered as a pre-packaged virtual machine, such as a virtual firewall or intrusion prevention system, that runs on virtualization or cloud platforms instead of dedicated hardware.
Is a virtual appliance as secure as a hardware appliance?
It can be, when correctly sized, patched and isolated, but it shares host resources, so hypervisor security and resource allocation are critical parts of its overall security.
Can I use a virtual appliance in the public cloud?
Yes, many vendors offer cloud marketplace images for major providers, but you should verify support, performance and licensing for your chosen cloud and region.
What is the difference between a virtual appliance and a cloud-native firewall?
A virtual appliance is portable software you manage across platforms, while a cloud-native firewall is a managed, provider-specific service integrated with that cloud’s controls.
When should I choose a virtual appliance?
Choose one when you need consistent security across hybrid or virtualized environments, fast deployment without hardware, and segmentation for traffic that physical appliances cannot see.