
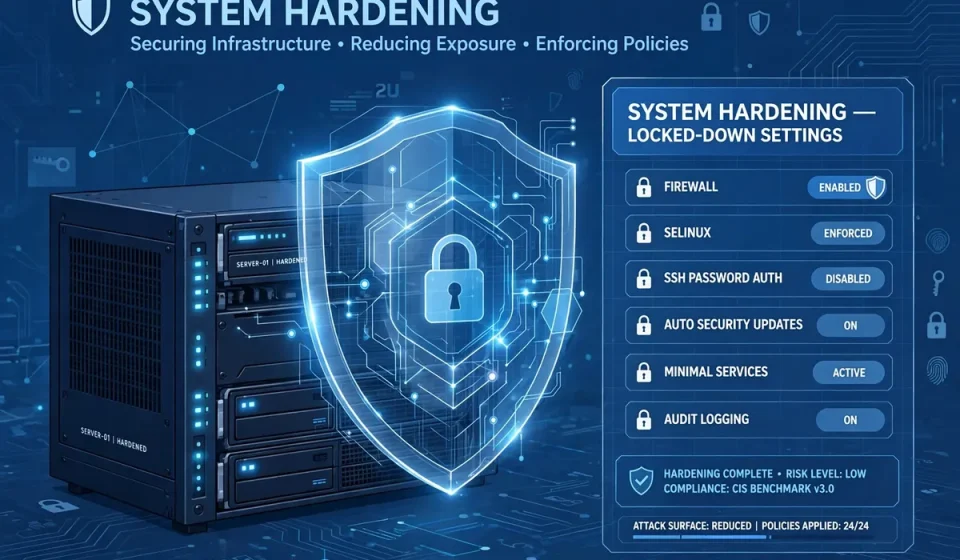

System hardening is the process of securing a system by reducing its attack surface: removing what is unnecessary, closing what should not be open, fixing weak settings, and enforcing strong controls. In plain terms, hardening turns a system that was shipped to be convenient into a system that is built to be defended. The default settings on most operating systems, servers and cloud services are designed to work out of the box, not to be secure, and attackers know exactly which defaults to try first.
This guide explains what system hardening is, the main types, and a practical checklist you can use for Windows, Linux, servers and cloud systems, plus a priority matrix and a 30-day rollout plan that most guides do not include.
What Is System Hardening?
System hardening means configuring a system so that it does only what it needs to do, with only the access it needs, and with every unnecessary door closed. The US National Institute of Standards and Technology (NIST) and the Center for Internet Security (CIS) both publish hardening guidance, and their benchmarks are the standard most organisations measure against. CIS Benchmarks cover Windows, Linux, cloud platforms, databases and network devices, giving a concrete, testable list of settings to apply.
Hardening is not a product you buy, and it is not a one-time project. It is a discipline: every new system starts from a secure baseline, every change is checked against that baseline, and drift is detected and corrected. A hardened system is also easier to monitor, because there is less noise, fewer services running, and a clearer picture of what normal looks like.
Why Hardening Matters: Attack Surface
Every service, port, account and piece of software on a system is a potential entry point. A server running ten services has ten things an attacker can probe, while a server running two has only two. Default passwords, guest accounts, old protocols and unused applications are the classic openings, and they feature in breach after breach. Vulnerabilities are harder to exploit when the vulnerable service is not running at all, and when the account an attacker would need has no unnecessary privileges.
Hardening also limits the damage when something does go wrong. If a web server is compromised but the database is on a separate, hardened host with only the needed port open, the attacker has further to go. That defence in depth is the real value of hardening: it buys time, raises the cost of attack, and makes detection more likely.
The Main Types of System Hardening
| Type | What it covers | Examples |
|---|---|---|
| Operating system | Windows, Linux, macOS | Patching, disabling services, secure boot |
| Network | Firewalls, routers, switches | Closing ports, segmenting networks |
| Server and application | Web, mail, database servers | Secure headers, least privilege, logging |
| Cloud | AWS, Azure, Google Cloud | Public bucket checks, IAM roles, encryption |
| Database | SQL, NoSQL databases | Authentication, encryption, auditing |
| Endpoint | Laptops, phones, IoT | Disk encryption, endpoint protection |
Most systems need more than one type. A cloud-hosted web application, for example, needs operating system hardening on its virtual machines, network hardening on its security groups, application hardening on its web server, and database hardening on its data store. The checklist below is organised by layer so you can work through it systematically.
System Hardening Checklist
Operating system hardening
Start with the basics. Apply all security patches and keep automatic updates on where safe. Remove or disable unused software, services and drivers, and uninstall applications nobody uses. Disable default and guest accounts, enforce strong passwords and multi-factor authentication, and require accounts to lock after a small number of failed logins. Enable full-disk encryption, such as BitLocker on Windows or LUKS on Linux, and enable secure boot with a BIOS or UEFI password. Finally, configure host firewalls to block all inbound traffic by default and allow only approved ports.
Network hardening
Close open ports and disable insecure protocols such as Telnet, SMBv1 and LLMNR. Segment the network so that sensitive systems are isolated from general user traffic, and use firewalls between segments. Protect management interfaces by restricting them to a separate network or a VPN, and encrypt traffic in transit. For traffic between sites, use IPsec tunnels with strong encryption, rather than sending data in the clear.
Access and identity hardening
Apply the principle of least privilege: give every user and service only the access it needs to do its job, and nothing more. Use role-based access control so permissions follow job roles, not individual requests. Remove standing administrator access where possible, use separate accounts for administration, and review privileged accounts regularly. Disable accounts promptly when people leave, and audit who has access to what at least quarterly.
Application and data hardening
Keep applications and their libraries patched, and remove default accounts and sample data from applications and databases. Configure secure headers, disable directory listing, and store secrets in a vault rather than in code or configuration files. Encrypt sensitive data at rest and in transit, back it up regularly, and test restoring from those backups. Enable logging for authentication, privilege changes and configuration changes, and send logs to a central system where they cannot be altered by an attacker.
What to Harden First: A Priority Matrix
Most teams cannot harden everything at once. This matrix, which most guides omit, helps you decide the order by weighing security impact against effort.
| Action | Impact | Effort | Do it |
|---|---|---|---|
| Patch critical flaws | High | Low | Immediately |
| Remove default passwords | High | Low | Immediately |
| Enable MFA for admins | High | Low | Week 1 |
| Disable unused services | Medium | Low | Week 1 |
| Apply CIS Benchmarks | High | Medium | Weeks 2 to 4 |
| Segment the network | High | High | Plan for next quarter |
| Replace legacy systems | High | High | Plan and budget |
Start with high impact and low effort, and you will remove the most common attack paths in days. The high effort items matter too, but they belong in a planned project, not in a rushed weekend.
A 30-Day System Hardening Plan
Week 1 is for discovery and quick wins. Inventory every system, account and service, apply critical patches, remove default credentials, enable multi-factor authentication for administrators, and close obviously unnecessary ports. Week 2 is for baselines: choose a CIS Benchmark for each system type, apply its settings in a test environment, and document any exceptions with a reason and an owner.
Week 3 is for rollout. Apply the baselines to production in stages, starting with the least critical systems, and monitor for problems. Week 4 is for verification: run a vulnerability scan and a configuration audit, compare the results with your baseline, fix drift, and schedule the next review. Repeat the audit monthly, and re-baseline whenever a system changes, so hardening does not quietly undo itself.
Common Mistakes That Undo Hardening
The most common mistake is hardening once and never checking again. Systems drift: someone opens a port for a test and forgets to close it, a new application needs an exception that never expires, or a patch resets a setting. Regular configuration audits and automated compliance checks catch drift before attackers do.
Other mistakes include hardening without testing, which can break applications and lead to settings being rolled back wholesale, and hardening only the servers while ignoring laptops, cloud accounts and network devices. Exceptions are another trap: every exception should have an owner, an expiry date and a compensating control, or it will become permanent. Finally, remember that hardening does not replace patching, backups or monitoring. It works with them, not instead of them.
Frequently Asked Questions
What is system hardening in simple terms?
System hardening is the process of making a computer system more secure by removing unnecessary software and services, closing open ports, fixing weak settings, and enforcing strong access controls, so attackers have fewer ways in.
What are some examples of system hardening?
Examples include applying security patches, disabling unused services, removing default passwords, enabling multi-factor authentication, turning on disk encryption, and configuring firewalls to block traffic by default.
What is the difference between hardening and patching?
Patching fixes known vulnerabilities in software. Hardening is broader: it includes patching, but also configuration, access control, removing unnecessary features and reducing the attack surface.
What are CIS Benchmarks?
CIS Benchmarks are consensus-based configuration guides from the Center for Internet Security for operating systems, cloud platforms, databases and network devices. They give a concrete, testable list of secure settings.
How often should systems be hardened?
Hardening should be continuous. Apply a secure baseline to every new system, audit configurations monthly, and re-check after any significant change, patch or new application.
Conclusion
System hardening is not glamorous, but it is one of the highest-value security activities there is. Every unnecessary service you remove, every default password you change, and every port you close is an attack path that no longer exists. Start with the quick wins, work through a recognised benchmark, and keep checking for drift. A hardened system will not stop every attack, but it will make most of them fail early, quietly, and far from your most important data.

[…] of individual permissions. RBAC also enforces least privilege by design, which is a core part of system hardening, and it reduces the impact of a compromised account, because the account only has the permissions […]
[…] The first is hardening — the systematic work of making systems secure by default. Our guide to system hardening explains the process in detail. The second is access control: most breaches involve stolen or […]