
What is a GPO? A GPO, or Group Policy Object, is a collection of settings that controls what users and computers can do on a Windows network. Managed through Active Directory, a single GPO can set password rules, install software, configure firewalls, map drives, and lock down desktops — for one department or for an entire organisation. Instead of configuring hundreds of computers one by one, an administrator defines the rules once, links them to the right group of machines, and lets Active Directory apply them automatically.
If you manage Windows computers at work, or you are studying for a networking or security certification, GPOs are one of the most practical tools you will meet. This guide explains what a GPO is, how Group Policy works, what you can control with it, and the best practices that keep it from becoming a mess.
What Is a GPO in Simple Terms?
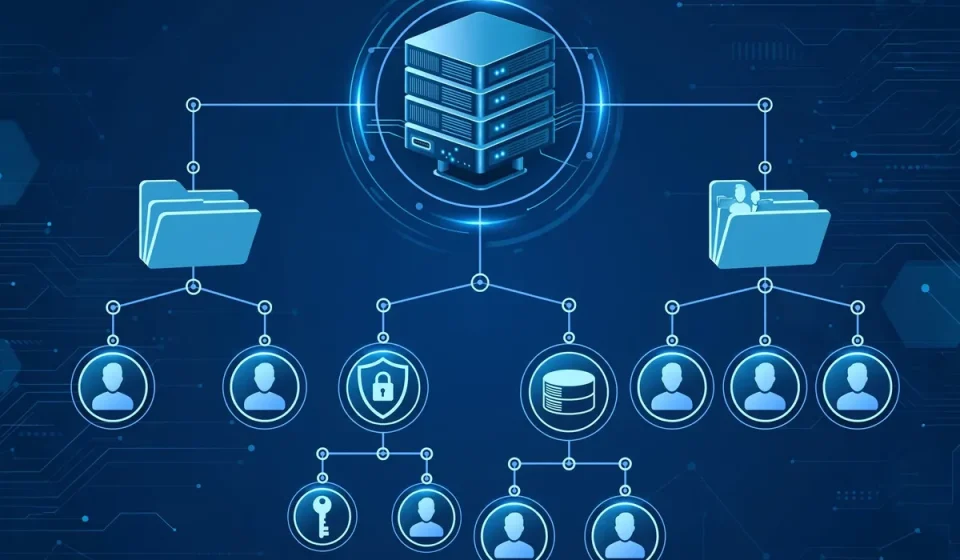
A Group Policy Object is a virtual container for configuration settings. Think of it as a rulebook. Each rulebook is stored in Active Directory, linked to a site, domain, or organisational unit (OU), and applied to the users and computers in that container.
When a computer starts up, and when a user signs in, Windows checks which GPOs apply, downloads the settings, and enforces them. If a setting conflicts with what a user tries to do — for example, a GPO disables USB storage — Windows blocks the action, even if the user is a local administrator on that machine.
Group Policy has two main parts. Computer Configuration settings apply to the machine itself, regardless of who signs in: things such as firewall rules, startup scripts, and installed software. User Configuration settings apply to the person who signs in: things such as desktop settings, mapped drives, and folder redirection. A single GPO can contain either or both.
How GPOs Work
Understanding a few building blocks makes the whole system click into place.
Active Directory and organisational units
Group Policy only works at scale because of Active Directory (AD). AD organises users and computers into a hierarchy of domains and OUs, such as “Finance”, “Sales”, or “Laptops”. A GPO linked to the Finance OU applies to finance users and computers, and nowhere else. This is how one company can give different rules to different departments without touching each machine.
The Global Catalog in Active Directory helps domain controllers find objects across the forest, but the day-to-day work of Group Policy happens at the domain and OU level.
Linking and inheritance
GPOs are linked to a container, and the computers and users inside that container inherit them. A GPO linked at the domain level applies to everything in the domain. A GPO linked to a child OU applies only there, in addition to the domain-level policies. If two linked GPOs set the same setting differently, the one linked closest to the user or computer — the child OU — wins.
Processing order: LSDOU
Policies are applied in a fixed order, remembered by the acronym LSDOU: Local, Site, Domain, Organisational Unit. Local policy on the machine is applied first, then site, then domain, then OU. Later policies override earlier ones when they conflict, so OU-level settings have the final say. Two exceptions change this: a GPO set to Enforced cannot be overridden by lower levels, and Block Inheritance stops policies from higher levels reaching a particular OU.
When policies apply
Computer settings apply when a machine starts, and user settings apply when a user signs in. After that, Group Policy refreshes in the background, typically every 90 minutes with a random offset of up to 30 minutes. An administrator can force an immediate refresh with the command gpupdate /force on a client machine.
What Can a GPO Control?
The range is wide, which is why GPOs are so powerful — and why a careless change can cause a lot of damage. Common uses include:
- Security settings: password length and complexity, account lockout after failed sign-ins, audit policies, and Windows Firewall rules.
- Software: installing, updating, or removing applications across many computers at once.
- Windows settings: disabling Control Panel items, restricting access to the registry or command prompt, and setting the desktop wallpaper and screen saver.
- Drive and printer mapping: connecting network drives and shared printers automatically when a user signs in.
- Folder redirection: moving Documents and Desktop folders to a network share, so files are backed up centrally.
- Scripts: running logon, logoff, startup, and shutdown scripts.
Group Policy Preferences add a further layer: they let administrators set drive mappings, shortcuts, printers, and registry values as preferences that users can change, rather than as policies that are enforced.
How to Create a GPO: Step by Step
Creating a GPO is straightforward, but it should always be done carefully and tested before it reaches production.
- Open the Group Policy Management Console (GPMC) on a domain controller or a management workstation with the Remote Server Administration Tools installed.
- Right-click the OU you want the policy to apply to, and choose “Create a GPO in this domain, and Link it here.” Give the GPO a clear, descriptive name, such as “Finance – Password Policy”.
- Right-click the new GPO and choose Edit. The Group Policy Management Editor opens, showing Computer Configuration and User Configuration.
- Browse to the setting you need — for example, Computer Configuration, Policies, Windows Settings, Security Settings, Account Policies, Password Policy — and configure it.
- Close the editor. The GPO is now linked and will apply at the next refresh, sign-in, or restart.
- Test it on a small OU or a test computer first. Use
gpresult /ron the client to confirm which policies applied, and the Group Policy Results wizard in GPMC for a full report.
Never edit the Default Domain Policy or the Default Domain Controllers Policy for routine changes. Create a new GPO instead, so you can disable or delete it cleanly if something goes wrong.
Troubleshooting GPOs
When a setting does not apply, the cause is usually one of a handful of issues. Working through them in order saves a lot of time.
- It has not refreshed yet: run
gpupdate /forceand sign out and back in, or restart the computer for computer settings. - Wrong scope: the GPO is linked to a different OU, or the computer or user object is not in the OU you think it is.
- Security filtering: the GPO applies only to the security groups listed on its Scope tab. Check that the computer or user is in one of those groups.
- Blocked inheritance or Enforced: check whether a parent policy is blocked, or a conflicting policy is enforced at a higher level.
- DNS and connectivity: clients must be able to find a domain controller and reach the SYSVOL share. DNS problems are a common root cause.
The Resultant Set of Policy (RSoP) tool and gpresult /h report.html produce a readable report of every policy that applied, and every one that was denied, with the reason. Lightweight Directory Access Protocol (LDAP) is the protocol clients use to read directory information, so LDAP or directory connectivity faults can also stop policies applying.
Best Practices for Managing GPOs
Most GPO problems are not technical; they are organisational. A few habits keep a Group Policy environment healthy.
- Name GPOs clearly. Use a naming convention that says what the GPO does and who it applies to, such as “All Users – Screen Lock 15 Minutes”.
- One purpose per GPO. A GPO that does ten unrelated things is hard to troubleshoot and dangerous to disable. Split settings by purpose.
- Test before deploying. Link a new GPO to a test OU with a few machines first, and watch for a day before linking it more widely.
- Back up GPOs regularly. Right-click a GPO in GPMC and choose Back Up. A backup is the fastest recovery from a bad edit.
- Audit regularly. Review linked GPOs at least once a year, and remove ones that are no longer needed.
Network security depends on consistent configuration across every machine, and GPOs are one of the main ways Windows environments achieve that consistency. Many organisations also use cloud tools such as Microsoft Intune for laptops that rarely visit the office; map your existing GPOs first, and migrate them in groups, testing each one as you go.
Frequently Asked Questions
What does GPO stand for?
GPO stands for Group Policy Object. It is a collection of settings that controls the working environment of user accounts and computer accounts in an Active Directory domain.
What is the difference between Group Policy and a GPO?
Group Policy is the overall feature and infrastructure in Windows and Active Directory. A GPO is a single object within that system — one set of settings, with its own name, link, and scope.
How often are GPOs applied?
Computer settings apply at startup and user settings at sign-in, and both refresh in the background about every 90 minutes. You can force a refresh immediately with gpupdate /force.
Conclusion
A GPO is the main way administrators manage Windows computers at scale. One object, linked to the right OU, can enforce password rules, deploy software, configure firewalls, and lock down desktops across hundreds of machines — and a single careless edit can do the opposite just as quickly. Learn the processing order, test every change in a small OU first, name your policies clearly, and back them up.