
Telnet is one of the oldest protocols on the internet — and one of the least safe. Every keystroke, username and password sent over Telnet travels in plain text, readable by anyone who can see the traffic. If you still need Telnet for a legacy device or an old application, you must encrypt that traffic or replace Telnet entirely. This guide shows you how to encrypt Telnet traffic: with SSH tunnels, VPNs, TLS wrappers, and the secure alternatives that should replace Telnet for good.
Why Telnet Traffic Needs Encryption
Telnet, defined in 1969 and standardised in RFC 854, was designed for a trusted academic network. It provides remote terminal access over TCP port 23, but it has no encryption, no real authentication security, and no integrity checking. When you log in over Telnet, your username and password cross the network as readable text. Every command you type and every byte of output does the same.
Anyone on the same network segment, anyone operating a router in the path, and anyone running a packet sniffer on a shared or compromised network can capture a Telnet session in full. That is why security standards, compliance frameworks and every modern network guide say the same thing: do not use Telnet on any network you do not fully control, and preferably do not use it at all.
Yet Telnet refuses to die. Old routers, switches, industrial controllers, mainframes, laboratory equipment and embedded devices often offer Telnet as their only remote management interface. Replacing the hardware is not always possible, so the practical question becomes: how do you encrypt Telnet traffic?
Can You Encrypt Telnet Directly?
Strictly speaking, plain Telnet has no built-in encryption. There is no switch you can flip on a standard Telnet client or server to make it secure. The protocol simply was not designed for it. That leaves three approaches: wrap the Telnet connection inside an encrypted tunnel, carry it across an encrypted network (a VPN), or stop using Telnet and use a protocol that encrypts by design.
The right choice depends on your situation. If you control both ends, replace Telnet with SSH. If a legacy device only speaks Telnet, tunnel it through SSH or a VPN. If you must expose Telnet across an untrusted network, a VPN is usually the cleanest answer.
| Method | Security | Difficulty | Best for |
|---|---|---|---|
| SSH tunnel | Strong — AES encryption | Moderate | One user reaching one legacy device |
| VPN | Strong — IPsec or WireGuard | Moderate | Whole teams or sites reaching legacy systems |
| Telnet over TLS (stunnel) | Strong — TLS encryption | Moderate to high | Applications that must keep using Telnet |
| Replace with SSH | Strongest, simplest long term | Low to moderate | Any system that supports SSH |
| Serial console / out-of-band | Strong — no network exposure | Varies | Data-centre and lab equipment |
Method 1: Encrypt Telnet with an SSH Tunnel
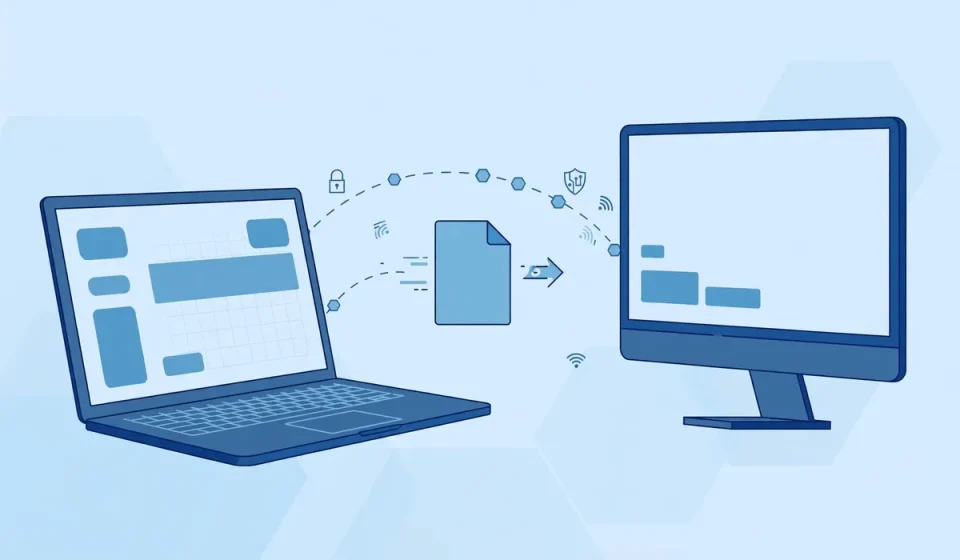
An SSH tunnel wraps your Telnet session inside an encrypted SSH connection. The Telnet traffic itself is still plain text, but it only ever travels in plain text on the local loopback interface of your own machine and on the short hop inside the remote host. Everything crossing the network is encrypted by SSH.
Suppose a legacy server at 192.168.10.50 only accepts Telnet on port 23, and you can SSH into a jump host at 192.168.10.10. From your workstation, run:
ssh -L 2323:192.168.10.50:23 user@192.168.10.10 -N
This tells SSH to listen on your local port 2323 and forward anything sent there, through the encrypted SSH connection, to port 23 on the legacy server. Then, instead of telnetting to the server directly, you connect to your own machine:
telnet localhost 2323
The Telnet client talks to the SSH client on your own computer; SSH encrypts the data, sends it to the jump host, and the jump host delivers it to the legacy server. An attacker watching the network sees only an SSH session. On Windows, the same thing is possible in PuTTY: open Connection, then SSH, then Tunnels, add a local forwarded port (source port 2323, destination 192.168.10.50:23), connect, and then Telnet to localhost 2323.
For this to work, you need an SSH server somewhere that can reach the Telnet device. That is usually a Linux server, a jump host, or a modern network device on the same segment. If no SSH server exists in that segment, a VPN is the better option. Keep the tunnel’s security in mind too: use SSH key authentication rather than passwords, and restrict which users can create tunnels.
Method 2: Encrypt Telnet with a VPN
A virtual private network encrypts everything between two points, so Telnet traffic inside the VPN is protected along with everything else. This is the best option when several people or several systems need to reach legacy Telnet devices, or when the Telnet traffic must cross the internet or another untrusted network.
With a site-to-site VPN, two networks are joined by an encrypted tunnel — typically IPsec — and Telnet sessions flow inside it as ordinary internal traffic. With a client VPN, a remote worker connects to the office network first, and then uses Telnet as if they were on site. Either way, the Telnet packets are encrypted between the VPN endpoints, and they never appear in plain text on the untrusted network.
Our guide to IPsec: what it is and how it works explains the protocol most site-to-site VPNs use, and our guide to site-to-site VPN covers the setup choices. When choosing a VPN for this purpose, prefer modern, audited protocols — WireGuard or IPsec with strong ciphers — and make sure the VPN gateway, not the Telnet server, is the only thing exposed to the untrusted network. A VPN does not fix Telnet’s other weaknesses: anyone who can join the VPN can still see the plain-text Telnet traffic inside it, so combine the VPN with strict access control and network segmentation.
Method 3: Telnet over TLS with Stunnel
Stunnel is a small program that wraps any plain-text TCP service in TLS — the same encryption that protects HTTPS. You run stunnel on the Telnet server (or on a proxy in front of it) and on the client, and it encrypts the connection between them. The Telnet application itself does not change: it still speaks plain Telnet to stunnel on localhost, and stunnel handles the encryption.
A minimal server-side stunnel configuration listens on a TLS port, decrypts the traffic, and forwards it to the local Telnet service. A matching client-side configuration accepts plain Telnet locally and forwards it over TLS to the server. You need a certificate for the server — a self-signed certificate works for internal use, but a certificate from your internal certificate authority is better, because the client can then verify the server’s identity and detect a man-in-the-middle attack.
There is also a Telnet STARTTLS extension (RFC 2946) that negotiates TLS inside a Telnet session, but support for it is rare in clients and servers, so stunnel is the practical choice in almost every case. Stunnel adds complexity — certificates to manage and another service to monitor — so prefer an SSH tunnel or a VPN unless an application genuinely requires a Telnet endpoint.
Method 4: Replace Telnet with SSH (The Best Option)
Whenever possible, the right answer is not to encrypt Telnet — it is to stop using it. SSH was designed as Telnet’s secure replacement, and it does everything Telnet does, with encryption, strong authentication and integrity checking built in.
| Feature | Telnet | SSH |
|---|---|---|
| Encryption | None — plain text | AES / ChaCha20 encryption |
| Authentication | Plain-text passwords | Passwords, keys, certificates, MFA |
| Port | 23 | 22 |
| Integrity | None | Message authentication codes |
| File transfer | No (use FTP, also insecure) | SCP and SFTP built in |
| Tunnelling | No | Port forwarding built in |
Replacing Telnet with SSH usually means enabling the SSH service on the device, creating key-based logins, and then disabling Telnet. On Linux servers this is a standard task; on network equipment, most vendors have supported SSH for many years and document the switch. For file transfers, the same logic applies: replace FTP with SFTP, as explained in our guide to what SFTP is and how it works. After the switch, verify that Telnet is really off — scan the device and confirm port 23 is closed — and remove Telnet clients from user workstations so nobody falls back to it by habit.
Securing Legacy Devices That Only Speak Telnet
Some equipment genuinely cannot run SSH: old industrial controllers, medical devices, laboratory instruments and embedded systems with firmware that will never be updated. For those, the goal is to make Telnet unreachable except through a controlled, encrypted path.
- Isolate the device. Put it on a dedicated VLAN or management network with no route to the internet and no access from ordinary user networks.
- Put a jump host in front of it. Only the jump host can reach the device’s Telnet port. Administrators SSH into the jump host first, then Telnet from there — or use an SSH tunnel as described above.
- Block port 23 at the firewall. Deny Telnet everywhere except from the jump host, and log any attempt to connect to port 23. Those logs are an early warning of scanning or misuse.
- Use strong, unique credentials. Even inside an encrypted tunnel, a weak Telnet password is a risk. Use a long random password, stored in a password manager, and change it when staff change.
- Plan the replacement. Record the device, its owner, and the date it will be retired or replaced. Legacy Telnet devices are technical debt: the longer they live, the more they cost in compensating controls.
Out-of-band management is another option for data-centre equipment: a serial console server or a dedicated management interface lets you reach a device without putting Telnet on the network at all.
How to Verify Your Telnet Traffic Is Encrypted
Do not assume the tunnel works — test it. Run a packet capture tool such as Wireshark or tcpdump on the network path between your workstation and the remote network, start a Telnet session through your tunnel or VPN, and look at the captured packets. You should see only SSH or VPN traffic — encrypted payloads with no readable usernames, passwords or commands. If you can read your Telnet password in the capture, the traffic is not going through the tunnel.
Also verify the failure mode: stop the SSH tunnel or disconnect the VPN, and confirm that the Telnet session cannot connect at all. A setup that silently falls back to plain Telnet when the tunnel drops is worse than no tunnel, because it creates a false sense of security. Firewall rules that block direct Telnet access enforce the encrypted path and make this failure mode impossible.
Frequently Asked Questions
Can Telnet be encrypted?
Plain Telnet has no encryption of its own. You encrypt Telnet traffic by wrapping it in an encrypted tunnel — an SSH tunnel, a VPN, or a TLS wrapper such as stunnel — or by replacing Telnet with SSH, which encrypts by design.
Is Telnet over SSH safe?
Yes, when done correctly. An SSH tunnel encrypts everything between your machine and the SSH server. Keep the segment between the SSH server and the Telnet device short, trusted and isolated, use key-based SSH authentication, and block direct Telnet access at the firewall.
What port does Telnet use, and should I close it?
Telnet uses TCP port 23. Yes — close it wherever possible. If a legacy device needs Telnet, block port 23 at the firewall for everyone except the jump host or VPN gateway that is allowed to reach it, and log connection attempts.
What is the difference between Telnet and SSH?
Telnet sends everything, including passwords, in plain text and has no integrity checking. SSH encrypts the whole session, supports key and certificate authentication, checks message integrity, and adds secure file transfer and tunnelling. SSH is Telnet’s secure replacement in every respect.
Can I use Telnet safely on a local network?
Only if you fully trust every device and person on that network segment and the traffic never leaves it — which is rarely true on a modern network with Wi-Fi, guest devices and flat topologies. Even locally, an SSH tunnel or a management VLAN is cheap insurance.
Is there a secure version of Telnet?
There is no widely used “secure Telnet”. The practical secure equivalents are SSH for terminal access and Telnet-over-TLS via stunnel for applications that cannot be changed. Both are well supported and far easier to defend than plain Telnet.
Conclusion
Telnet’s problem is not a bug — it is the design. A protocol that sends passwords in plain text cannot be made safe by a firewall rule alone. If you can replace Telnet, replace it with SSH. If a legacy device gives you no choice, tunnel the traffic through SSH or a VPN, isolate the device on its own segment, block port 23 for everyone else, and verify with a packet capture that nothing readable crosses the network. Do that, and the oldest protocol on your network stops being the easiest way in.