
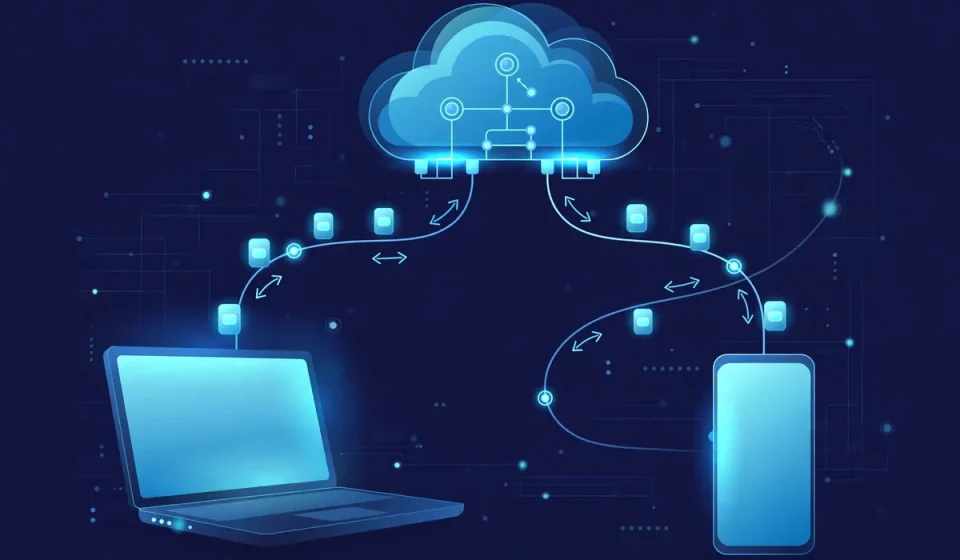

When you check the weather on your phone, book a flight online, or log in to a cloud dashboard, different systems are talking to each other behind the scenes. In most cases, they use a REST API. But what is REST API technology, exactly, and why has it become the standard way for software to share data over the internet?
What Is a REST API?
A REST API is a way for two pieces of software to communicate over the web using the rules of REST, or Representational State Transfer. REST is an architectural style created by Roy Fielding in 2000. An API, or application programming interface, is a set of rules that lets one application request data or services from another. Put together, a REST API lets a client, such as a website or mobile app, ask a server for a resource, such as a user profile or a weather forecast, and receive a response, usually in JSON format.
Unlike a website designed for people to read, a REST API is designed for machines to read. It does not return a styled web page. It returns structured data that another program can use or display. That is why the same API can power a website, an iPhone app, and an Android app at the same time.
How Does a REST API Work?
A REST API works through a simple request and response cycle. The client sends an HTTP request to a unique web address, called an endpoint. The server processes that request, checks whether the client is allowed to see the data, and sends back an HTTP response with a status code and, usually, the requested data.
The Client Sends a Request
Every request has four main parts. First, the method, which says what action to take. Second, the endpoint, or URL, which identifies the resource. Third, headers, which carry extra information such as the data format or an authentication token. Fourth, an optional body, which carries data when creating or updating a resource.
The Server Sends a Response
The server answers with a status code that shows whether the request succeeded, and a body that contains the result. A successful request for a single user might return a JSON object with that user’s name, email address, and account type. An unsuccessful request might return an error message, such as a missing resource or invalid credentials.
The Six Principles of REST
For an API to be truly RESTful, it should follow six principles. First, client-server separation: the user interface and data storage stay independent. Second, statelessness: each request must contain all the information the server needs, because the server does not remember previous requests. Third, cacheability: responses should say whether they can be stored and reused, which improves speed. Fourth, a uniform interface: resources are identified by URLs and manipulated through standard methods. Fifth, a layered system: the client need not know whether it is talking to the final server or an intermediate layer, such as a load balancer. Sixth, code on demand, which is optional: a server may send executable code to extend what the client can do.
HTTP Methods Used by a REST API
REST APIs use standard HTTP methods to describe the action. The table below shows the most common methods, what each one does, and a typical example.
| Method | Action | Example |
|---|---|---|
| GET | Retrieve a resource | GET /users/42 returns one user profile |
| POST | Create a new resource | POST /users creates a new user account |
| PUT | Replace a resource completely | PUT /users/42 replaces that user profile |
| PATCH | Update part of a resource | PATCH /users/42 changes only the email address |
| DELETE | Remove a resource | DELETE /users/42 deletes that user account |
GET requests are safe and repeatable: asking for the same data twice should give the same result and should not change anything. POST, PUT, PATCH, and DELETE change data, so they need stronger protection, covered in the security section below.
REST vs SOAP vs GraphQL
REST is not the only way to build an API. SOAP is an older, strict protocol that uses XML messages and detailed contracts. It is powerful for enterprise systems, but heavier and harder to learn than REST. GraphQL, developed by Meta, lets a client ask for exactly the fields it needs in a single query, which can reduce over-fetching of data, but it can be more complex to secure and cache. REST remains the most popular choice for public and cloud APIs because it is simple, widely understood, works well with HTTP, and is easy to test.
Understanding HTTP Status Codes
Status codes tell the client what happened at a glance. Codes in the 200s mean success, such as 200 OK and 201 Created. Codes in the 300s mean redirection. Codes in the 400s mean a client error, such as 400 Bad Request, 401 Unauthorized, 403 Forbidden, and 404 Not Found. Codes in the 500s mean a server error, such as 500 Internal Server Error. Learning these codes makes debugging faster, because you can tell whether the problem is in your request, your permissions, or the server.
A Worked Request and Response Example
Imagine a weather app asking a cloud service for the forecast in London. The request might look like this:
GET https://api.example.com/weather?city=London
Authorization: Bearer abc123token
Accept: application/json
The server might reply with a 200 OK status and this JSON body:
{
"city": "London",
"temperature_c": 14,
"condition": "Partly cloudy"
}
The app then displays that data to the user. Notice that the request never contains a web page, only the data the app needs, and the token in the header proves the app is allowed to use the service.
REST API Security Basics: The Angle Most Guides Miss
Most beginner guides explain what a REST API is but skip how to keep one safe. That gap matters, because an exposed API can leak data, allow account takeover, or let attackers overload a cloud service.
Authentication and Authorization
Authentication proves who you are, while authorization decides what you are allowed to do. A secure API should never trust a request just because it reached the server. It should check an API key or, preferably, a short-lived access token, and then check whether that identity has permission for the specific resource. For example, one user should never read another user’s private data simply by changing an ID number in the URL.
Tokens, HTTPS, and Rate Limiting
Tokens are safer than sending a password with every request. A common pattern is OAuth 2.0, where a user signs in once and the app receives a token that expires after a short time. Always use HTTPS, not plain HTTP, so tokens and data are encrypted in transit. Strong encryption is a core part of this protection, as explained in our guide to what AES encryption is and how it protects data. Finally, rate limiting caps how many requests a client can make in a given period, blocking brute-force attacks and overload. A good API returns a 429 Too Many Requests status when the limit is reached.
Input Validation and Least Privilege
Every input to an API should be checked before it is used, because attackers often send unexpected data to trigger errors or inject malicious commands. APIs should also follow least privilege, giving each key or token only the permissions it truly needs. These practices, combined with the broader controls in our top 10 cloud security best practices for 2026, greatly reduce risk from exposed endpoints. Application owners should also review who manages those controls, a role described in our guide to the application security manager and what that role does.
Benefits and Limitations of REST APIs
The main benefits of REST APIs are simplicity, scalability, and flexibility. They use familiar web standards, work with any programming language, and scale well because stateless requests can be handled by many servers. Their limitations include a lack of a strict built-in standard, which can lead to inconsistent designs, and the risk of over-fetching data, since a fixed endpoint may return more than a client needs. Good documentation, versioning, and security controls solve most of these problems.
Frequently Asked Questions
What is REST API in simple terms?
In simple terms, a REST API is a set of web-based rules that lets one application ask another application for data or services, and receive a structured answer, usually in JSON.
What is the difference between an API and a REST API?
An API is a general term for any interface that lets software communicate. A REST API is a specific type of API that follows the REST style, using HTTP methods, resource URLs, and stateless requests.
What format does a REST API use?
Most REST APIs use JSON because it is lightweight, easy to read, and supported by almost every programming language. Some older APIs use XML, but JSON is now the standard choice.
Is a REST API secure?
A REST API can be secure, but security is not automatic. It needs HTTPS encryption, strong authentication, short-lived tokens, authorization checks on every resource, input validation, and rate limiting.
When should I use REST instead of GraphQL?
Use REST when you need a simple, well-understood, cache-friendly API with standard HTTP tools and clear endpoints. Consider GraphQL when different clients need very different shapes of data from the same backend.
Conclusion
Now you know what a REST API is, how its requests and responses work, which HTTP methods to use, and why security must be built in from the start. Whether you are learning to code or choosing a cloud service, REST is the language most of the modern web speaks. Start with a simple GET request, study a public API’s documentation, and build from there.

[…] usually sit behind APIs, so their security depends on the API layer too. Our guide to what a REST API is explains how APIs work and how to protect […]